Your Business Deserves Concierge-Level Hosting.
Get In TouchRegister A Domain
hosting australia horizontal 002
logo only
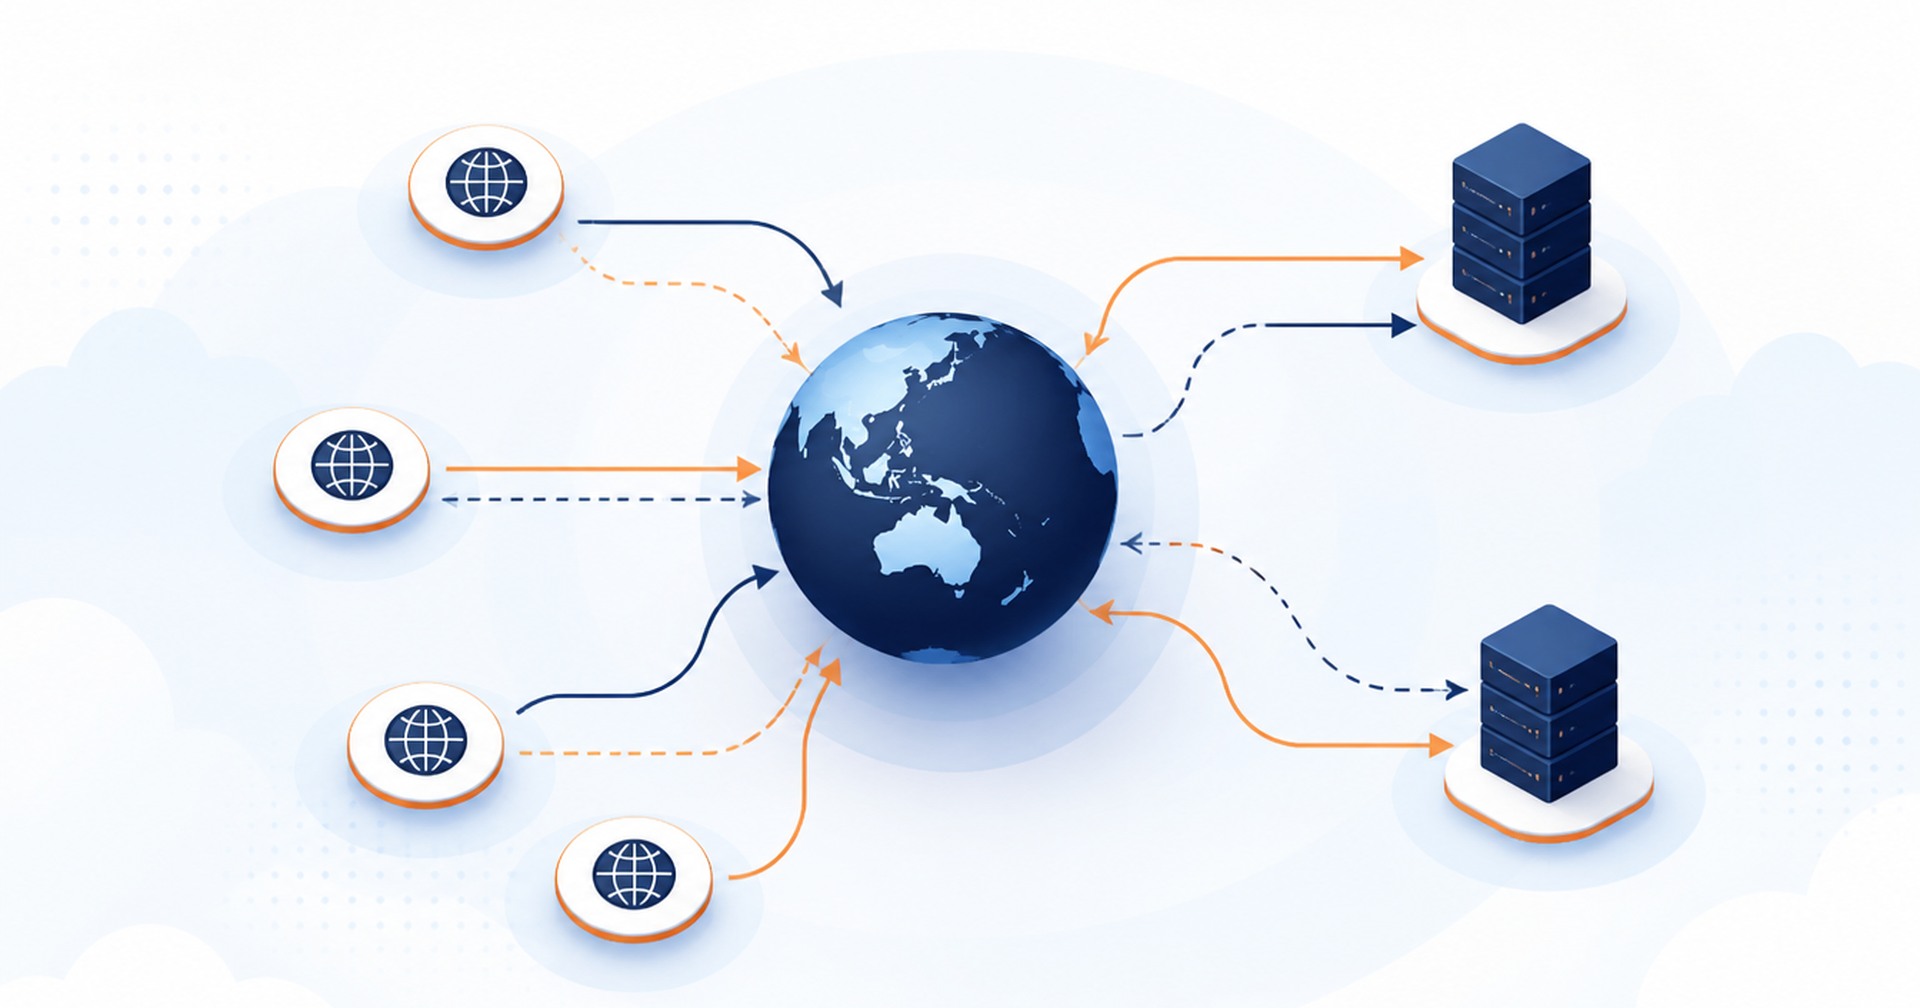
DNS propagation between global network nodes and servers

DNS Propagation Explained for Australian Small Businesses

Plan website and email DNS changes without guesswork

Prepare, change, verify: make DNS cutovers safer

After you change a website address, email provider or hosting service, one person may see the new service while another still reaches the old one. That uneven period is commonly called DNS propagation. For a small business, it can mean customers reaching an old site, mail going to the wrong system, or a launch appearing broken on some connections.

What DNS propagation really means

DNS changes are not pushed to every device at once. Your authoritative nameservers publish the current records. Recursive resolvers operated by internet providers, workplace networks or public DNS services look them up for users and keep copies in cache. The original DNS design in RFC 1034 uses distributed data and local caching rather than one instantly synchronised database.

When a resolver has an unexpired answer, it can return that value without asking your authoritative nameserver again. Another resolver may have no cached copy and fetch the new answer immediately. This is why a change can work on office internet but not on mobile data. Cloudflare's resolver documentation confirms that a recursive service contacts authoritative nameservers when its cache has no answer.

TTL is the main clock

Each DNS record has a time to live, or TTL, expressed in seconds. It tells resolvers how long they may cache that answer. A longer TTL improves the chance of a fast cached response, while also making later changes slower to appear. That trade-off is explained in Cloudflare's TTL reference.

The important value is the TTL attached to the old answer before you edit it. Lowering the TTL at the same moment as the destination will not shorten copies already cached under the previous, longer value. If a change is planned, reduce the relevant TTL at least one existing TTL period beforehand. Once the move is stable, return it to your normal setting rather than leaving an unusually short TTL indefinitely.

How different record changes behave

  • A records: These direct a hostname to an IPv4 address. During a hosting move, some visitors may reach the old server until their resolver's cached A answer expires. Keep both web servers ready and serving the same essential content during the transition where possible.
  • AAAA records: These provide an IPv6 address and are cached separately from A records. Updating only the A record can leave IPv6-capable visitors reaching the old server. Check whether the destination supports IPv6, then update or deliberately remove the AAAA record as part of the same plan.
  • CNAME records: A CNAME makes one name an alias of another. Resolution can involve the alias and its target, each with caching considerations. Confirm that the new target exists before changing the alias. Do not place other record types at the same hostname as a CNAME, a configuration issue covered by RFC 1912.
  • MX records: These direct incoming email to mail servers, with priority values deciding the preferred destination. During a change, sending systems may use either the old or new cached MX answer. Create mailboxes at the new provider first, preserve required TXT records for SPF, DKIM and DMARC, and keep the old mail service receiving mail until the cutover is confirmed.

A safe DNS change checklist

  • Identify the authority: Confirm which nameservers currently host the live zone. Editing a DNS panel that is not authoritative changes nothing for public users.
  • Record the starting point: Export the zone or capture every current value, TTL and priority. Include A, AAAA, CNAME, MX and email authentication records.
  • Prepare first: Configure the new website, certificate, redirects, mailboxes and third-party services before changing DNS. Test them using a temporary hostname or provider-approved method.
  • Lower TTL early: Reduce only the records involved, and do it at least one old TTL period before the cutover. Nameserver changes can involve separate delegation caching, so treat them as a broader change.
  • Choose a quiet window: Avoid a major promotion, payroll run or other business-critical period. Make one controlled set of edits and log the exact time and old values.
  • Keep a rollback path: Leave the previous web and mail services operational while cached answers expire. Know which values you will restore if testing fails.
  • Verify from several paths: Check the authoritative answer, more than one public resolver, office internet and mobile data. Test the website over HTTPS, forms, logins, and email in both directions.
  • Finish deliberately: After the old TTL window has passed and checks are clean, restore the intended TTL, retire the old service carefully, and save the final zone record.

When waiting will not fix it

Propagation is often blamed for configuration errors. If the authoritative nameserver already returns the wrong value, waiting only preserves the mistake. A missing record, CNAME conflict, incorrect MX priority, stale AAAA record, broken DNSSEC chain, or disagreement between authoritative nameservers needs correction. Also remember that browser, operating system, router and application caches can sit in front of the recursive resolver. Clearing one local cache may help your test, but it does not refresh caches used by customers.

When to ask hosting support

Ask for help before the change if you cannot identify the authoritative DNS provider, do not know which records belong to website or email services, are changing nameservers, or have DNSSEC enabled. Contact support promptly if authoritative servers disagree, queries return SERVFAIL, email stops flowing, HTTPS fails at the new address, or different results remain after the previous TTL should have expired. Provide the domain, record type, expected value, time changed and test results from more than one network.

If you want domain management backed by an Australian team, review Hosting Australia's domain registration and transfer options.

Plan for overlap, not instant change

A sound DNS change assumes a temporary overlap between old and new answers. Lower the TTL in advance, prepare both destinations, verify every affected record type and keep a rollback path. That turns propagation from an unpredictable outage risk into a controlled transition your business can test and monitor.
Back To News Page

Related Articles

How Do We Compare?
Take a look how we stack up against some of the bigger competitors!

Australian Hosting Support

Customer care for Australians, by Australians.
australian hosting support
(07) 4914 2433
best australian web hosting
Email & Ticket Support
australian web hosting chat
Live Chat
Newsletter Sign Up
logo only